In today’s fast-paced software development landscape, Continuous Integration and Continuous Deployment (CI/CD) pipelines are essential for delivering applications efficiently. However, the speed and automation they offer can inadvertently introduce security vulnerabilities if not properly managed. Integrating security into CI/CD pipelines, often referred to as DevSecOps, is no longer optional; it’s a necessity.
The Importance of Security in CI/CD
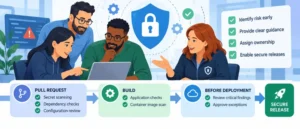
Traditional security practices often occur late in the development cycle, leading to delays and increased costs when vulnerabilities are discovered. By embedding security checks into the CI/CD pipeline, teams can identify and address issues early, reducing risk and maintaining development velocity.
Key Strategies for Integrating Security
Automated Security Testing Incorporate tools that automatically scan code for vulnerabilities during the build process. Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST) tools can identify common issues without manual intervention.
Dependency Management Use Software Composition Analysis (SCA) tools to monitor third-party libraries and dependencies for known vulnerabilities. Keeping dependencies up-to-date is crucial for maintaining a secure codebase.
Infrastructure as Code (IaC) Scanning As infrastructure is increasingly managed through code, it’s vital to scan IaC templates for misconfigurations that could lead to security breaches. Tools like Terraform and CloudFormation scanners can automate this process.
Secret Management Ensure that sensitive information, such as API keys and passwords, are not hardcoded into the codebase. Implement secret management solutions to handle credentials securely.
Continuous Monitoring and Feedback Establish monitoring systems that provide real-time feedback on security issues. This continuous feedback loop enables teams to respond quickly to new threats and maintain a strong security posture.
Conclusion
Integrating security into CI/CD pipelines is essential for modern software development. By adopting automated tools and practices, teams can proactively address vulnerabilities, ensuring that security keeps pace with rapid development cycles. Embracing DevSecOps not only protects your applications but also builds trust with users and stakeholders.
🍪 On respecte ta vie privée. On utilise des cookies de mesure d'audience (Google Analytics)
et, à terme, de la publicité. Rien n'est chargé sans ton accord.
En savoir plus.